
Play · Developers and platform teams
Govern MCP tools for every agent
Every tool call throughone URL is written down.
Claude, Cursor, Copilot and the agents you wrote all point at the gateway, and the upstream keys never leave it. A changed tool schema is held until someone looks, and every call through it lands as a row with the identity behind it.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF

- This play uses
- 01Discover
- 03Enforce
- 05Prove
Who
A platform team with a dozen MCP servers wired into Cursor, Claude, and three internal LangGraph agents, each with its own copy of the upstream keys.
What happened
An upstream MCP server shipped a changed tool definition overnight, and an agent used it for a day before anyone noticed.
What's at stake
Keys in config files, tools that can change what they do without notice, and no record of which agent called what on whose behalf.
- 01Discover
Inventory the tools from live connections, not a spreadsheet.
Point every client at the gateway and the registry fills from what actually connects: which upstreams, which tools, which agent and which person is behind each call. Each user authorizes their own upstreams with OAuth, so the inventory already knows who granted what. Every tool schema is fingerprinted the moment the gateway sees it.
one URL in front of every upstream · OAuth per user · schemas fingerprinted · registry from live connections
mcp gateway · home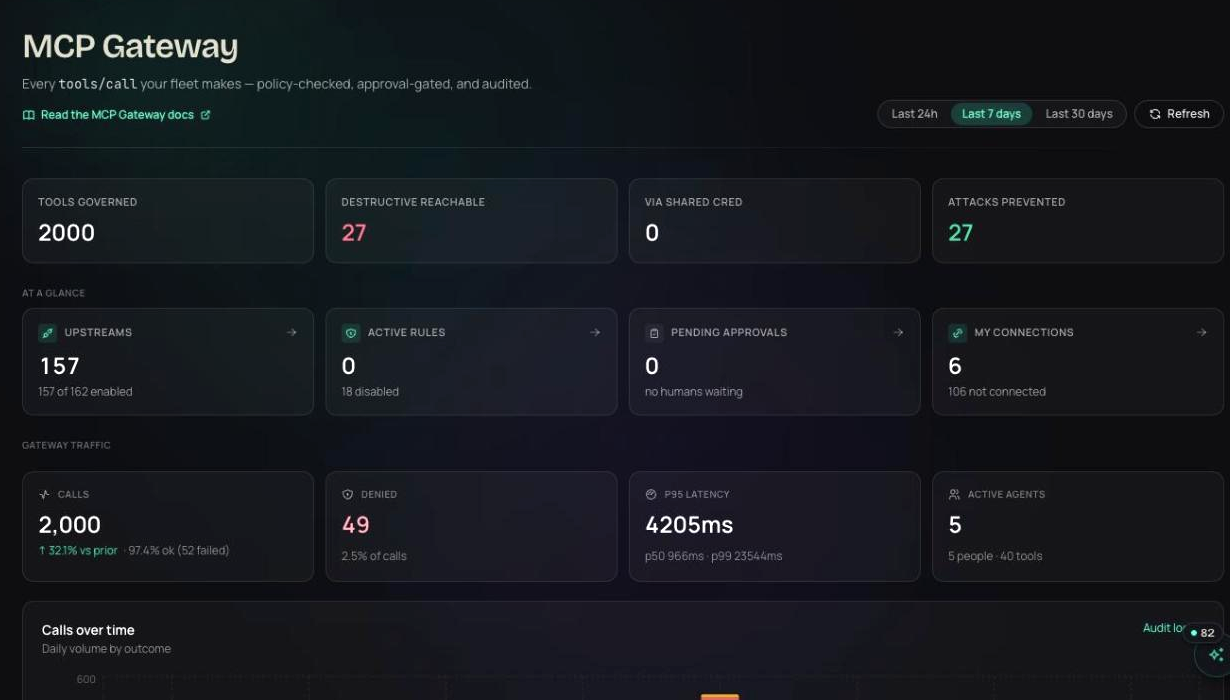
- 02Enforce
Policy on each call. Keys stay in the gateway.
Agents hold a scoped gateway token, never the upstream key. Each call is checked for scope, data class, rate, and whether it needs an approval; the answer is allow, redact, hold, or block, and there is an audit row either way. When an upstream changes a tool's schema, the fingerprint stops matching and calls to that tool are held until someone looks. Offboard a person and every grant they made goes with them.
scope · data class · rate · approval · changed tool held · offboard revokes every grant
mcp gateway · activity · live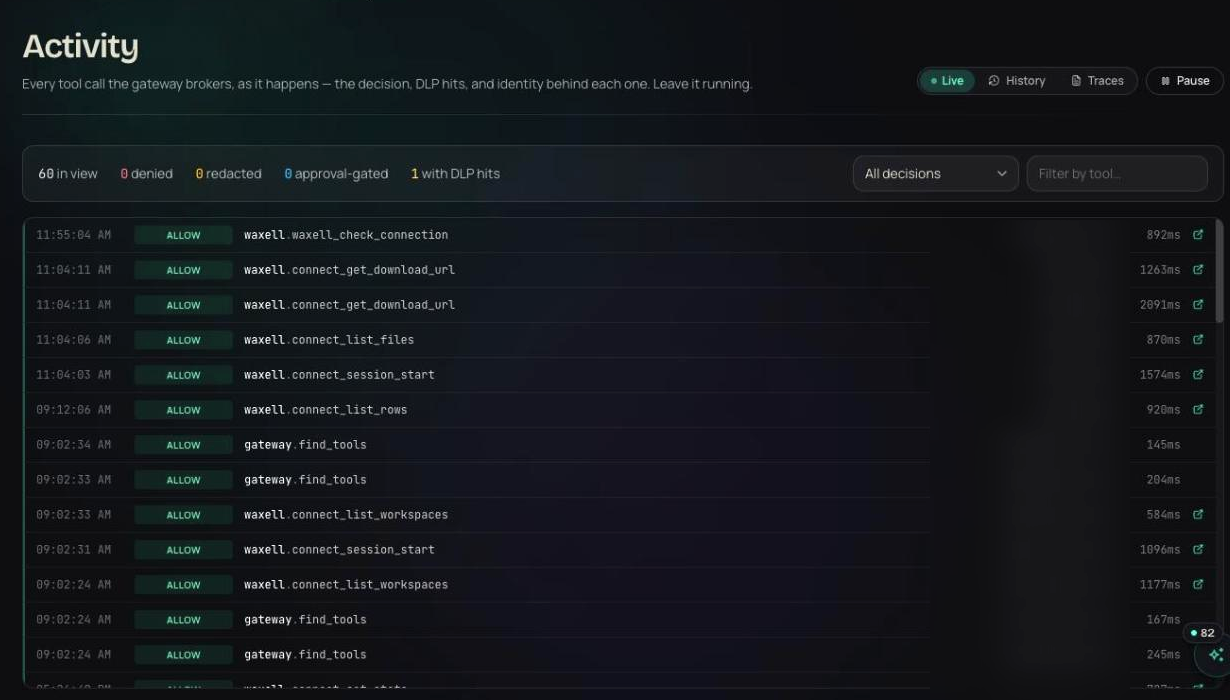
- 03Prove
The activity feed is the audit.
Every call is a row: the agent, the person it acted for, the tool, the verdict, the policy that spoke, and any DLP hit. Filter it for a security review, or export a compliance pack when the auditor asks what your agents can reach and who let them.
identity per call · DLP hits in the feed · signed compliance packs
insights · compliance pack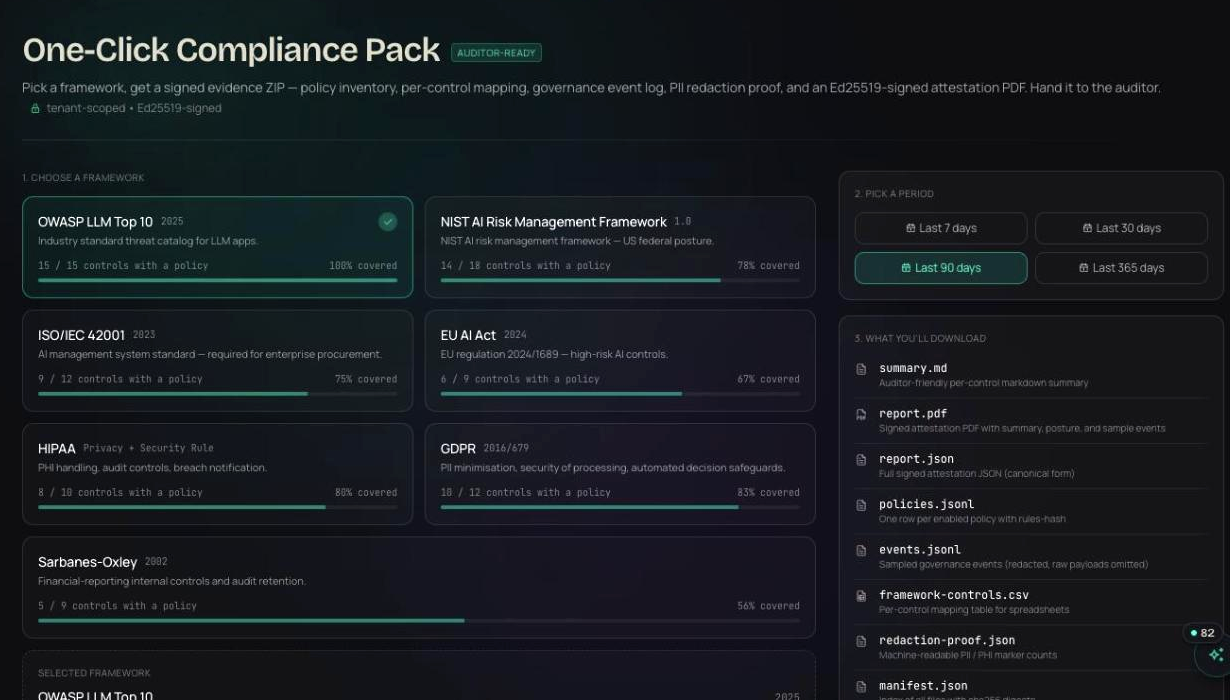


- github.create_pull_request · billing-apicursor · a.patel · scoped grant · write:prallow
- jira.search · 'customer email'ops-agent · for s.nguyen · PII in result · 3 emails maskedredact
- notion.export_page · 140 blocksclaude · m.okafor · tool schema changed since fingerprint · pending reviewhold
- slack.post_message · #generalops-agent · for s.nguyen · channel outside scopeblock
Illustrative entries in the shape the product writes them.
Products in this play
Only the URL. Claude, Cursor, Copilot, and LangGraph agents already speak MCP; point them at the gateway and keep the tool names. The upstream keys move into the gateway and out of your config files.
Run this play this week.
Free for your first agents and devices, live in about thirty seconds. Or walk through it with someone who has run it before.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF