
Play · Security teams
Govern coding agents in engineering
Coding agents onenrolled laptops,under one policy.
Claude Code, Cursor and Codex are already on engineering laptops, some on personal accounts. The endpoint agent finds them, puts a managed hook in front of each one, and checks pastes and uploads so a config file with a credential in it is stopped before it sends.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF

- This play uses
- 01Discover
- 03Enforce
- 05Prove
Who
A security team at a software company where engineering adopted coding agents faster than anyone wrote a policy for them.
What happened
A contractor's Cursor session on a personal account sent a config file with a production key in it to a model provider. Nobody knew until the key had to be rotated.
What's at stake
Credentials and source leaving through tools nobody inventoried, on accounts the company does not control, with no answer for the customer security questionnaire.
- 01Discover
Find the CLIs as well as the apps.
Coding agents live in terminals and editor extensions, not the dock. The endpoint agent reports Claude Code, Codex and Cursor per device, CLI sessions included, and whether each runs on a corporate or personal account. Device owners, set on the device or read from Hexnode, put a name beside every session. The Shadow AI report shows which teams run what.
desktop apps, CLIs and extensions · personal vs corporate accounts · device owners from Hexnode or the device page
endpoints · discovered apps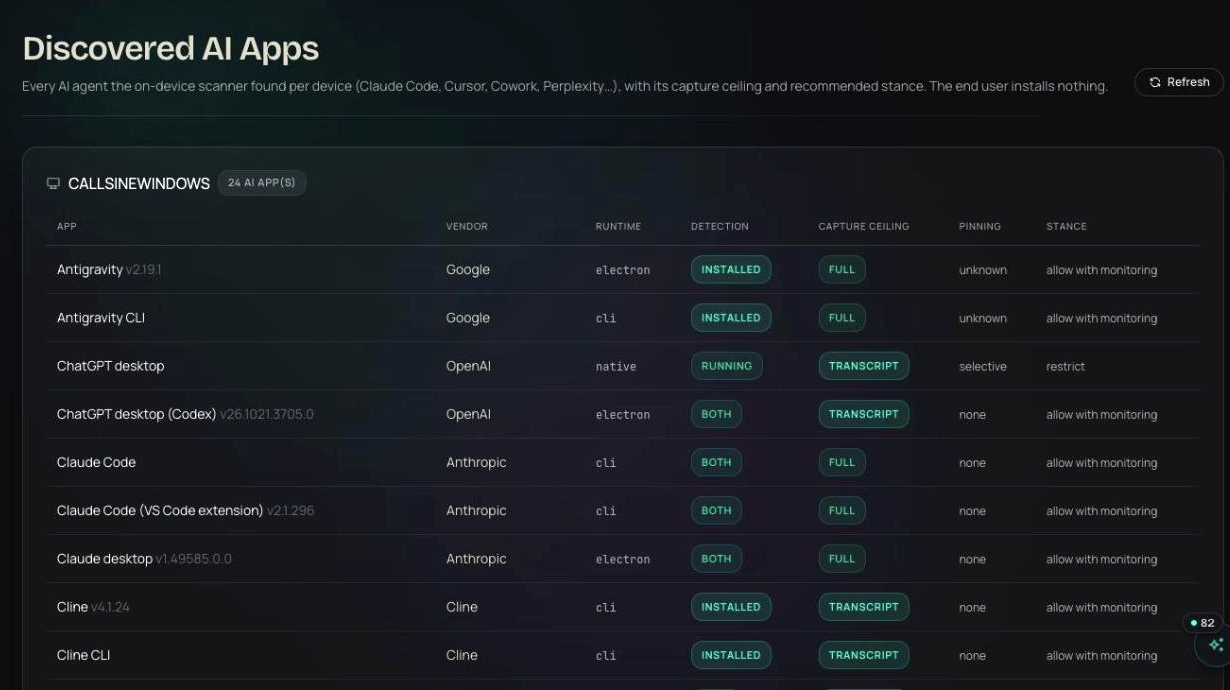
- 02Enforce
A hook before every action. Secrets stopped either way.
Waxell registers a managed hook in each coding agent's administrator-owned configuration, so Claude Code, Codex and Cursor check each command, file and prompt against the Guard before they act: allow, ask or deny. Set rules per app type, team or device. Agent DLP checks outgoing files and pastes, so a file with an API key, a connection string or a credential in it is stopped before it sends. A device that keeps tripping policy can be quarantined from the console.
managed hooks: allow / ask / deny · rules per app type, team or device · agent DLP · quarantine from the console
endpoints · needs attention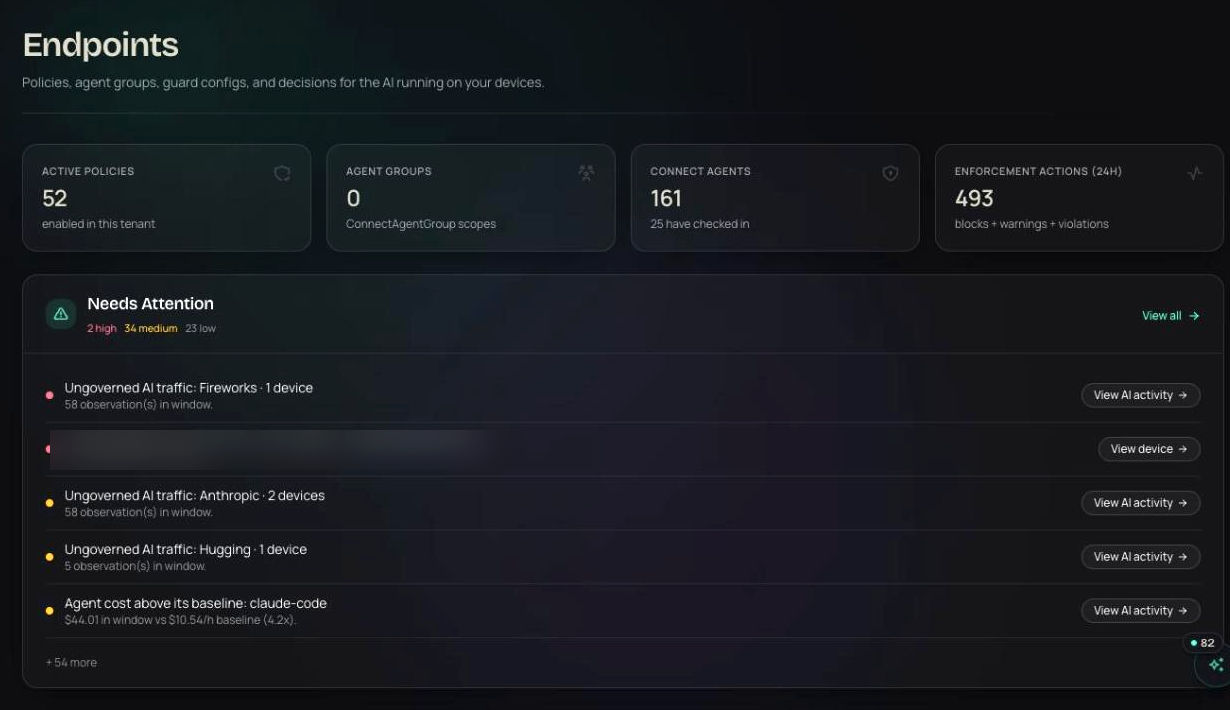
- 03Prove
Answer the security questionnaire with a query.
Every session start, every block and every classification is a decision with the policy behind it. When a customer asks how you govern AI coding tools, export the per-device evidence or a signed compliance pack mapped to the OWASP LLM Top 10.
per-device evidence · signed compliance packs · OWASP LLM Top 10
insights · compliance pack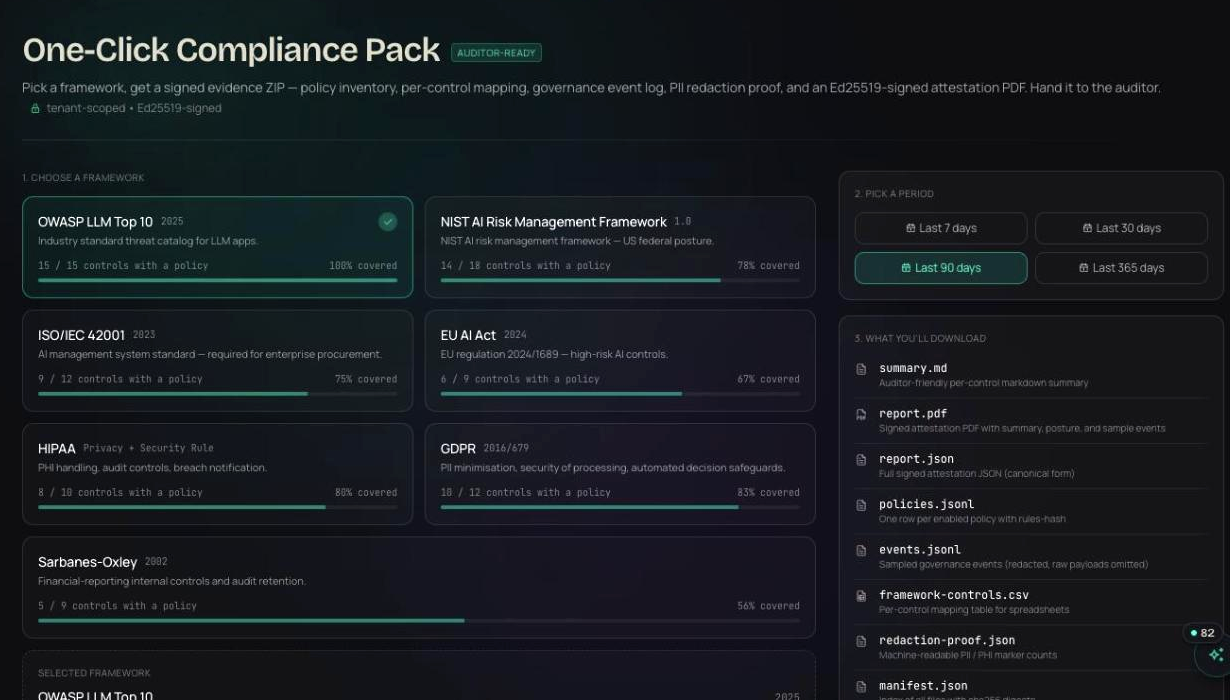


- Claude Code · corporate account · session startendpoints · k.diaz-mbp · corporate account · capture onallow
- Cursor · personal account · upload .envendpoints · contractor-07-win · credential pattern (AWS access key)block
- Codex · corporate account · paste 1,900 charsendpoints · p.ibarra-mbp · connection string detectedblock
- ai-autocomplete-plus · AI appendpoints · m.sato-mbp · not on the allowed apps listblock
Illustrative entries in the shape the product writes them.
Products in this play
No. A corporate-account session with nothing sensitive in it is allowed and recorded. Only an action your rules deny, or a paste or upload that matches a detector, is stopped.
Run this play this week.
Free for your first agents and devices, live in about thirty seconds. Or walk through it with someone who has run it before.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF