
Play · Security teams
Stop PII leaving through AI
The paste with thecustomer list is blockedby policy before it sends.
The endpoint agent checks prompts and uploads against DLP detectors as they leave the browser: credentials, card numbers, Social Security numbers, email addresses and the patterns you add. A paste that matches is blocked before it sends, and the block is a decision with the policy that made it.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF

- This play uses
- 01Discover
- 03Enforce
- 05Prove
Who
A security team at a company that handles customer records and has approved a handful of AI tools without a way to see what goes into them.
What happened
A support rep pasted a ticket export, names and card numbers included, into an AI chat to draft a reply. The tool was approved. The data was not.
What's at stake
PII and payment data sitting in a third-party model log, a breach-notification clock that may already be running, and no record of what went where.
- 01Discover
Know where prompts go before you decide what is in them.
The endpoint agent deploys through Jamf, Kandji, Intune, Hexnode or your RMM and the browser extension is force-installed by policy. Within hours you have every AI desktop app, coding agent and browser AI session per device, and whether each runs on a personal or corporate account. Every one of them is a path data can take. The Shadow AI report shows which paths are busiest.
AI apps, coding agents and browser AI · personal vs corporate accounts · macOS and Windows · Chrome, Edge, Firefox
endpoints · discovered apps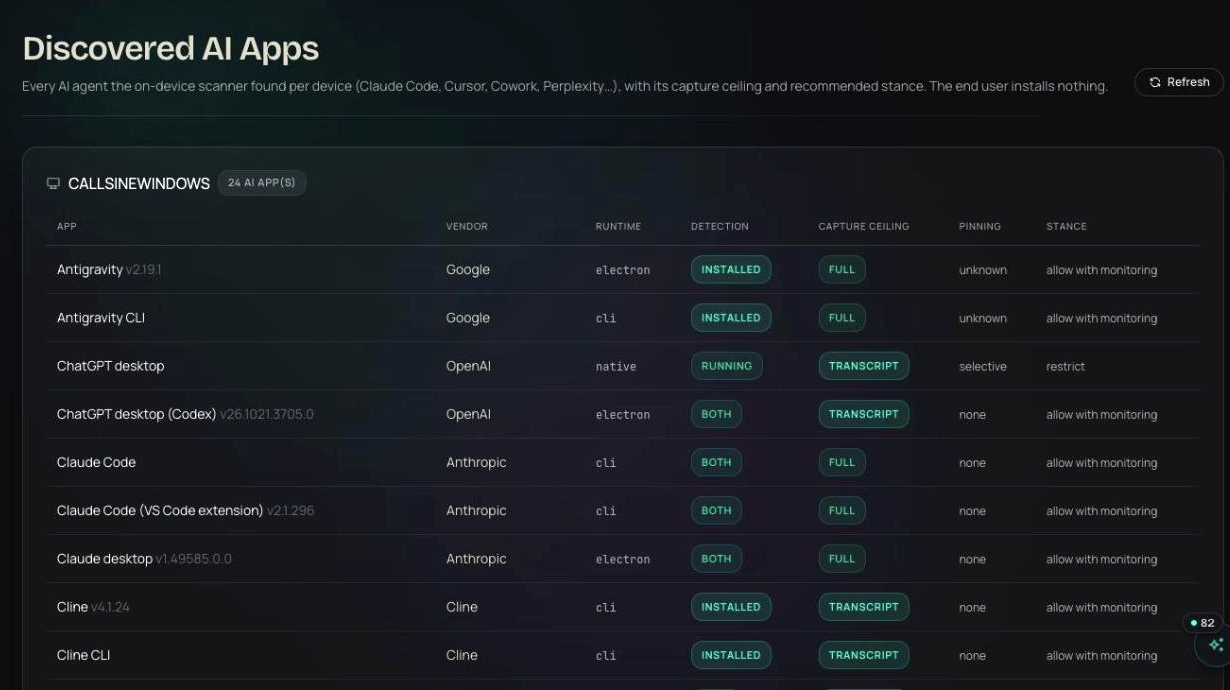
- 02Enforce
Classify at the edge. Block the record, keep the question.
Browser AI conversations are captured and uploaded by default, with secrets redacted on the device first; an admin can turn Browser capture off globally or for a team, app type or device. Set browser DLP to block and prompts and uploads are checked against DLP detectors: credentials, card numbers, Social Security numbers, email addresses, and patterns you add for your own formats. A match is blocked before it sends. A plain question goes through untouched, so nobody learns to route around the control. A device that keeps tripping policy can be quarantined from the console.
browser DLP: warn or block · built-in and custom detectors · per team, app type or device · quarantine from the console
endpoints · needs attention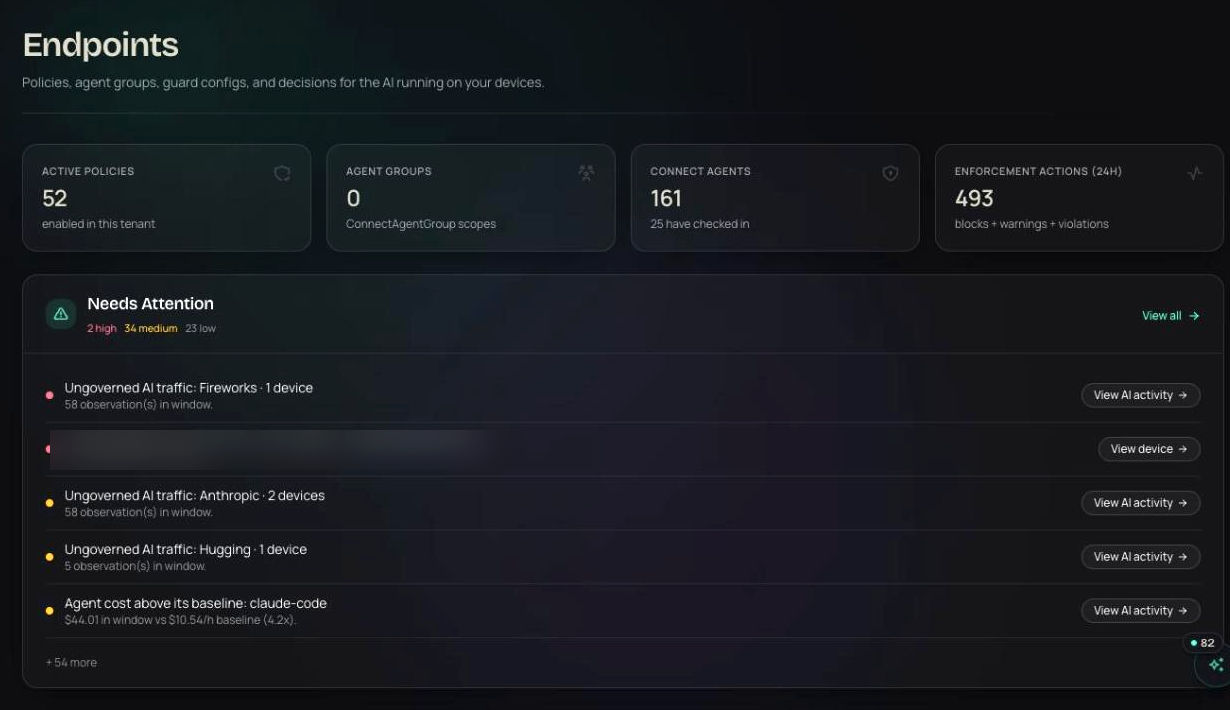
- 03Prove
The breach you can show never happened.
Every classification is a decision with the detector that fired, the device, the account and the tool. When legal asks whether customer data reached a model provider, the answer is a query, not an investigation. Export a signed compliance pack with the PII redaction proof and the governance event log, mapped to GDPR or HIPAA.
PII redaction proof · governance event log · Ed25519-signed attestation · GDPR and HIPAA mappings
insights · compliance pack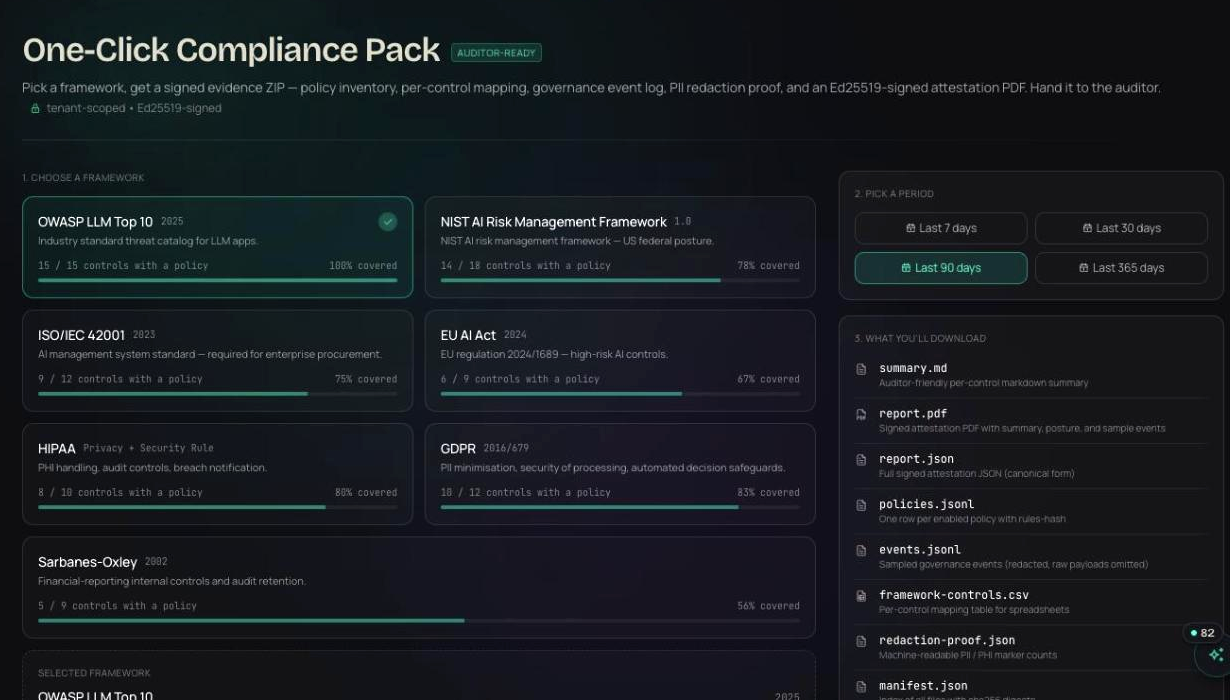


- ChatGPT · corporate account · upload tickets-export.csvendpoints · s.patel-mbp · credit card numbers (14)block
- ChatGPT · corporate account · prompt 410 charsendpoints · s.patel-mbp · no DLP detectors matchedallow
- Claude · personal account · paste 3,200 charsendpoints · a.nguyen-win · U.S. SSN pattern · personal accountblock
- Copilot · corporate account · upload q3-pipeline.xlsxendpoints · t.okafor-mbp · corporate account · no DLP detectors matchedallow
Illustrative entries in the shape the product writes them.
Products in this play
The built-in detectors cover credentials and API keys, payment card numbers (checksum-validated), U.S. Social Security numbers and email addresses. Add patterns for your own formats, such as an employee ID, and they apply to blocking and to redaction.
Run this play this week.
Free for your first agents and devices, live in about thirty seconds. Or walk through it with someone who has run it before.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF