
Play · Security teams
HIPAA-ready agents
PHI in the promptmeans the HIPAA profile,or no run.
Waxell is SOC 2 Type II attested and ISO/IEC 27001:2022 certified, supports HIPAA with a Business Associate Agreement, and is aligned to the EU AI Act and NIST AI RMF. The HIPAA compliance profile checks that the policies a PHI workload needs are on before an agent runs.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF

- This play uses
- 01Discover
- 03Enforce
- 05Prove
Who
A security team at a provider or health-tech company whose clinical and billing teams are deploying agents on Bedrock, Vertex and Azure AI Foundry.
What happened
A prior-authorization agent in Bedrock AgentCore was reading claims with PHI in them, and the compliance officer asked what assurance covered the tooling that watched it.
What's at stake
PHI moving through agents with no audited tooling around them, no retention commitment, and no proof that nobody saw it who should not have.
- 01Discover
Every agent that can reach PHI, in one registry.
The discovery connectors for AWS Bedrock AgentCore, Google Vertex and Azure AI Foundry inventory the agents your teams deployed. Bedrock onboards with a one-click cross-account role or an org-wide StackSet; Vertex onboarding is keyless. Each agent lands in the registry with an owner, a scope and its governance coverage, so a prior-auth agent with no policy shows up as dark.
Bedrock AgentCore, Vertex, Azure AI Foundry connectors · owner, scope, policy per agent · coverage: enforced / governed / observed / dark
agent discovery · overview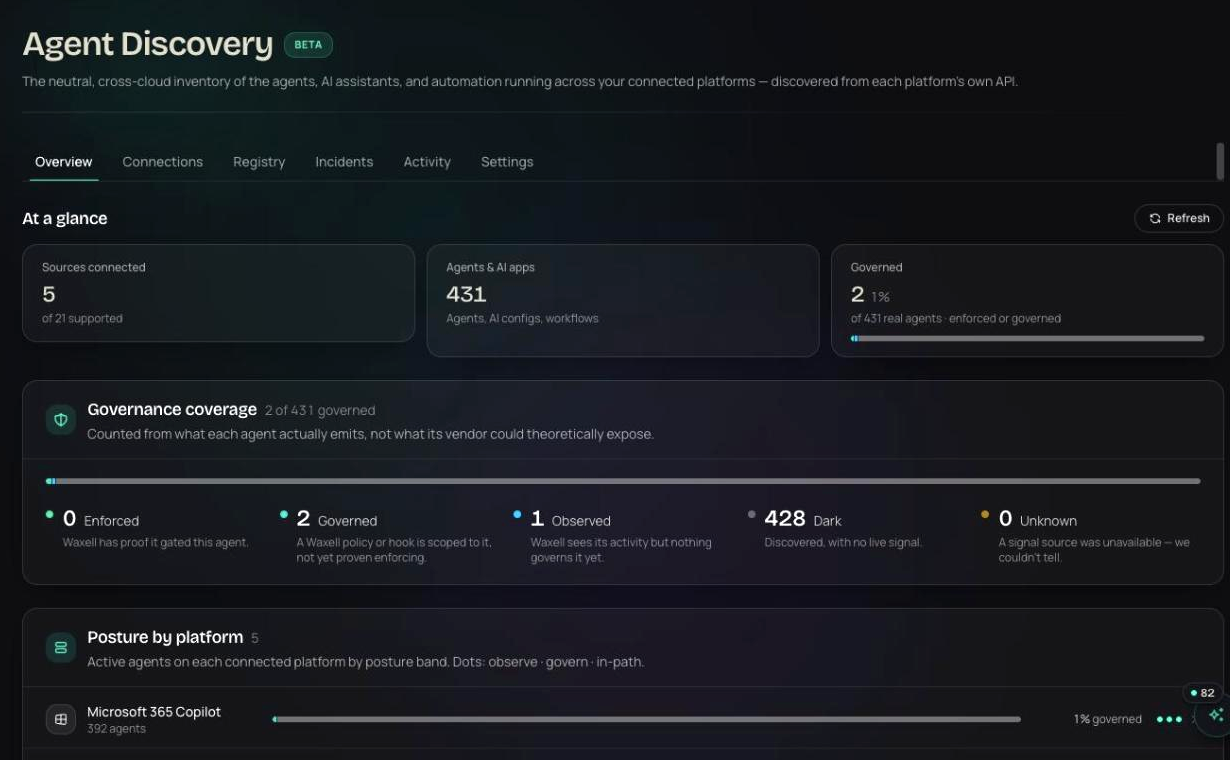
- 02Enforce
The HIPAA profile checks the siblings.
A compliance profile is a meta-policy. Turn on HIPAA for an agent and it checks that audit retention, PII detection and data access policies are in force before the agent runs; if one is missing, the run does not start. PHI in a prompt or a tool result is detected and redacted or blocked by policy. Waxell runs in the United States.
compliance profile: HIPAA · PII detection · audit retention
govern · policies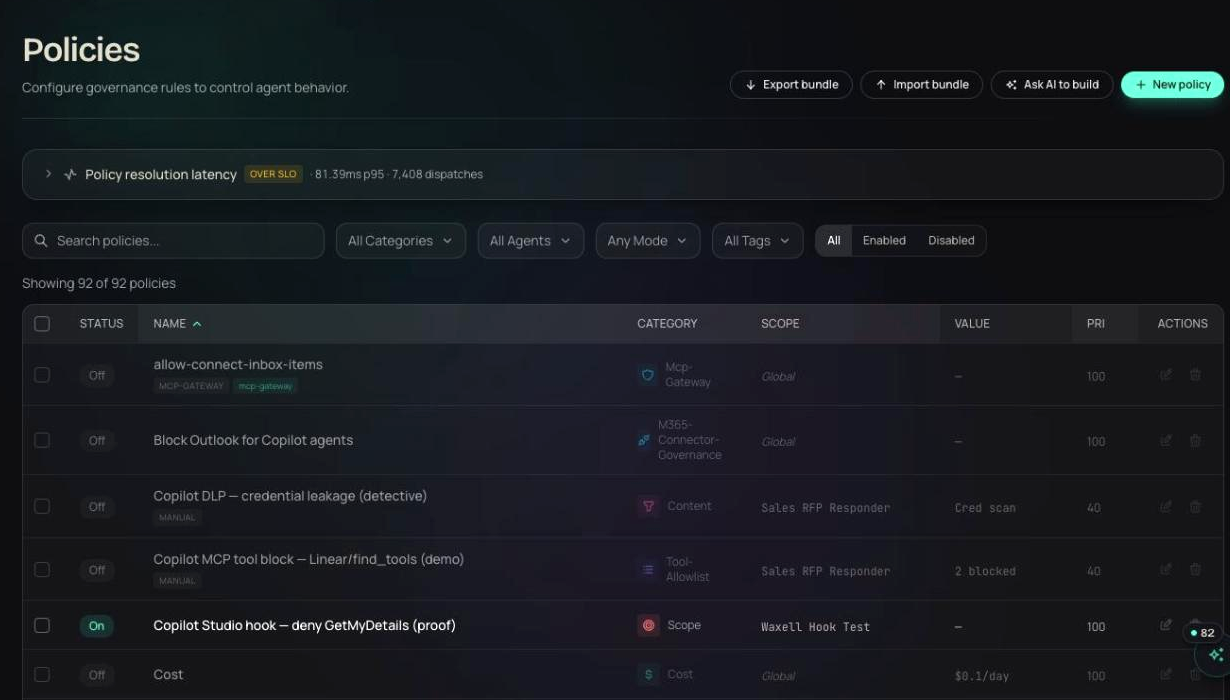
- 03Prove
An audited vendor, a pack for the auditor.
Waxell is SOC 2 Type II attested and ISO/IEC 27001:2022 certified, supports HIPAA with a Business Associate Agreement, and is aligned to the EU AI Act and NIST AI RMF. Support access to a regulated tenant needs written approval under the Business Associate Agreement and Regulated Services Addendum, subprocessors are a published list with notice before any change, and retention is configurable per data class up to seven years with legal hold. The compliance pack maps per control to HIPAA with the governance event log and the PII redaction proof, signed.
SOC 2 Type II · ISO/IEC 27001:2022 · HIPAA with a BAA · written approval for support access · published subprocessor list · HIPAA-mapped signed pack
insights · compliance pack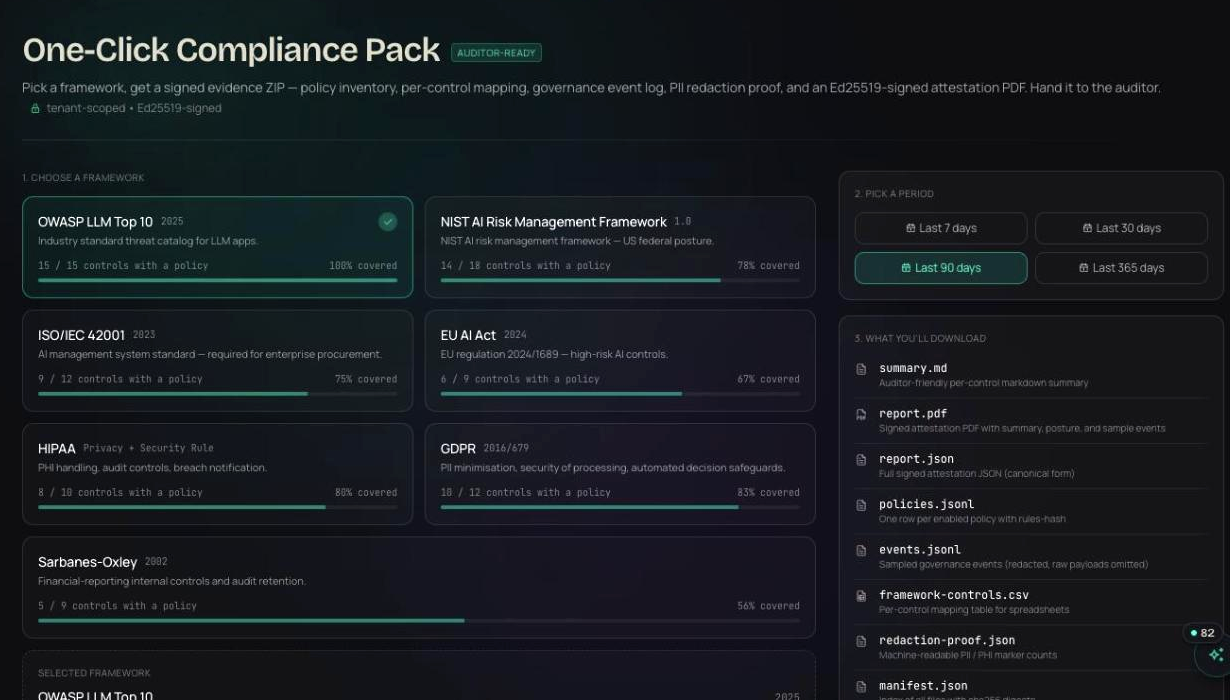


- run.start · compliance profile: HIPAAbedrock · prior-auth-agent · audit retention policy not on · run not startedblock
- claims.read · member 4471bedrock · prior-auth-agent · profile satisfied · data access scope: claimsallow
- tool.result · patient-notesvertex · intake-summarizer · PHI detected (MRN, date of birth) · redactedredact
- email.send · external recipientfoundry · billing-assistant · data egress · PHI in bodyblock
Illustrative entries in the shape the product writes them.
Waxell is SOC 2 Type II attested and ISO/IEC 27001:2022 certified, supports HIPAA with a Business Associate Agreement, and is aligned to the EU AI Act and NIST AI RMF. The Type II report is available under NDA from the Trust Center.
Run this play this week.
Free for your first agents and devices, live in about thirty seconds. Or walk through it with someone who has run it before.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF