
Play · Security teams
Discover agents across your clouds
The agents yourbusiness builtwithout you.
Business teams have been building agents in Copilot Studio, Foundry, Bedrock, Vertex and Agentforce for a year. Connect each platform once and each agent it reports lands in one registry with an owner, a scope, and whether it is enforced, governed, observed, or dark.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF

- This play uses
- 01Discover
- 05Prove
Who
A security team at a company on Microsoft 365 and AWS, with a Salesforce org and a Google Cloud project the data team runs.
What happened
An internal audit asked for a list of AI agents in production. Three teams sent three spreadsheets, and none of them agreed.
What's at stake
Agents with access to mail, CRM and customer data that nobody in security has seen, owned by people who may have left, with nothing to show the auditor.
- 01Discover
Connect each platform once.
Microsoft 365 Copilot and Copilot Studio, Azure AI Foundry, and Salesforce Agentforce each take one connector. AWS Bedrock AgentCore takes a one-click cross-account role, or an org-wide StackSet for every account at once. Google Vertex onboards keyless and covers Agent Engine, Dialogflow and Gemini Enterprise. Once connected, the registry lists every agent the platforms know about, with the platform it runs on, the owner it could find, and what the agent is wired to.
Copilot · Copilot Studio · Foundry · Bedrock AgentCore · Vertex · Agentforce · one registry
agent discovery · overview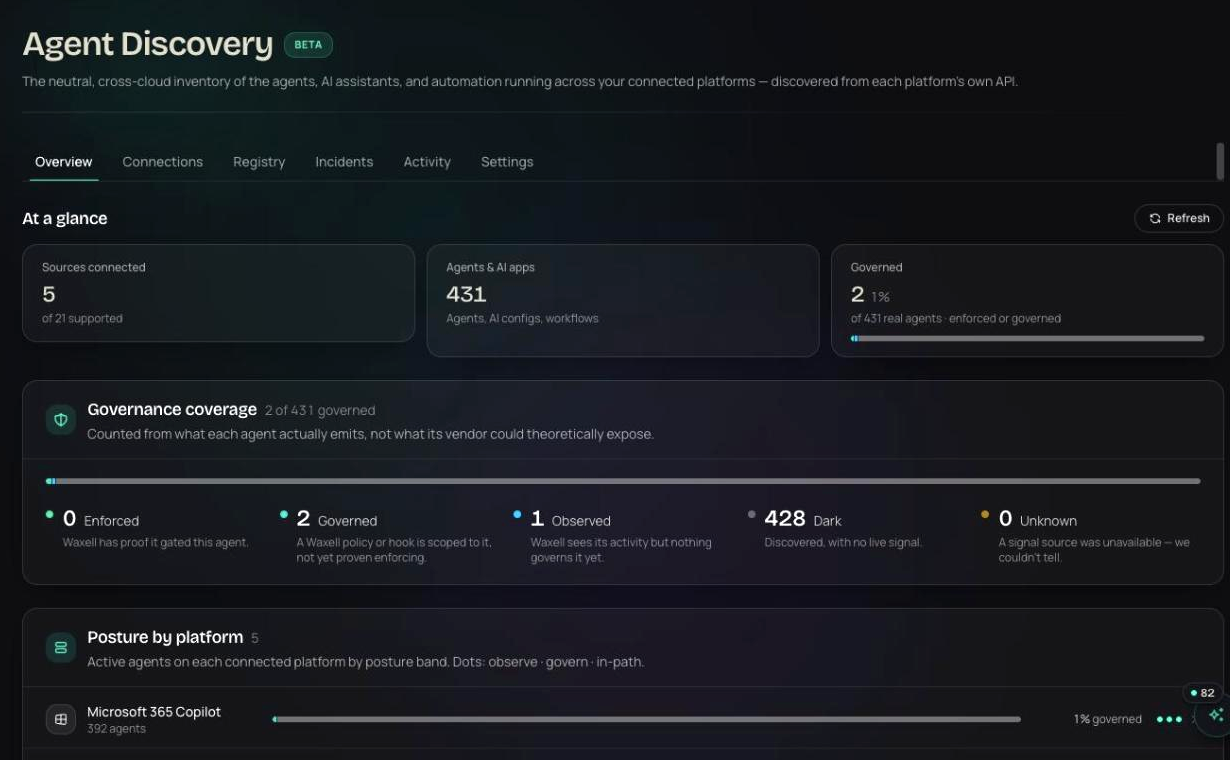
- 02Discover
An owner, a scope, and a coverage grade per agent.
Every agent in the registry gets an owner, a scope that says what it can reach, and a policy. Coverage is shown per agent: enforced, governed, observed, or dark. Dark is the list you take to the platform owners. The registry is the system of record the audit asked for, and it stays current because it is built from the platforms, not from a form.
owner · scope · policy per agent · coverage: enforced, governed, observed, dark
govern · overview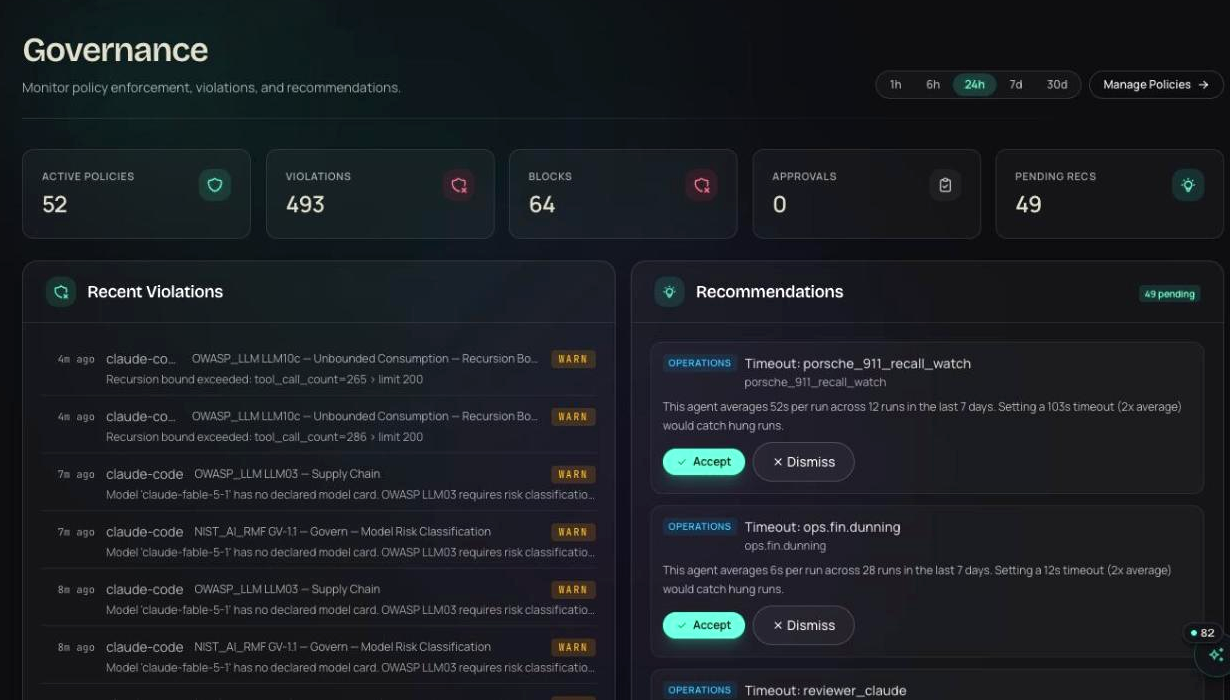
- 03Prove
One list, signed, that the auditor can reread next quarter.
Export the registry as part of a compliance pack: the agent inventory, the owner per agent, and the policy and coverage for each, with an Ed25519-signed attestation. NIST AI RMF GOVERN 1.2 asks for accountable roles; an owner on every agent is that control, with the evidence attached.
agent inventory in the pack · signed attestation · NIST AI RMF, ISO/IEC 42001, EU AI Act mappings
insights · compliance pack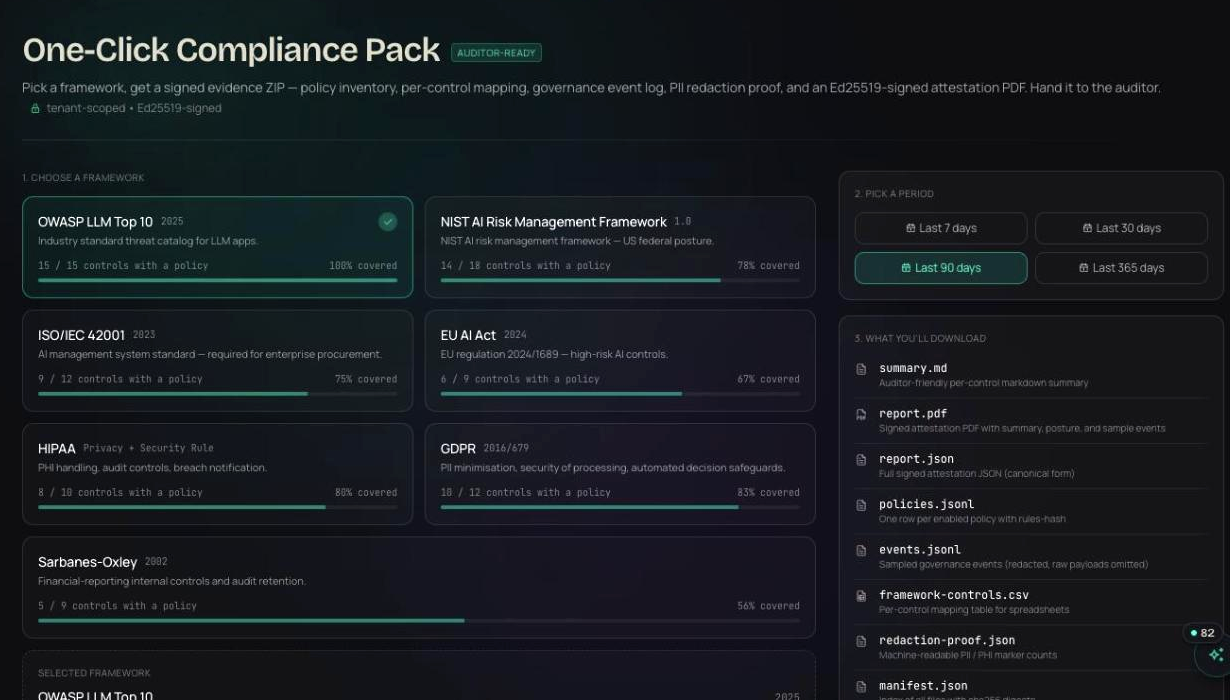


- discovered · owner k.ramos · scope: SharePoint Legalcopilot-studio · contracts-helper · governed · policy attachedallow
- discovered · reaches Service Cloud casesagentforce · case-triage · dark · no owner · review assignedhold
- discovered via StackSet · account 4412bedrock-agentcore · ops-runbook · observed · owner d.okaforallow
- discovered · Gemini Enterprisevertex-agent-engine · data-qna · scope unknown · pending ownerhold
Illustrative entries in the shape the product writes them.
Products in this play
Each connector onboards the way the platform supports. Bedrock AgentCore is a one-click cross-account role, or an org-wide StackSet for every account at once. Vertex is keyless. Copilot, Foundry and Agentforce each take one connector set up by the platform admin.
Run this play this week.
Free for your first agents and devices, live in about thirty seconds. Or walk through it with someone who has run it before.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF