
Play · Security teams
Govern Copilot Studio agents
The agent a businessteam built on Friday,in the registry by Monday.
The Microsoft 365 connector finds the Copilot Studio agents in the tenant and puts each in the registry with an owner. Governance hooks installed into each agent check each action against policy before it runs, and the record shows the denies.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF

- This play uses
- 01Discover
- 03Enforce
- 05Prove
Who
A security team at a Microsoft 365 shop where business teams build Copilot Studio agents without an intake process.
What happened
An HR agent built in Copilot Studio could call a GetMyDetails action that returned any employee's record, not only the asker's. Nobody reviewed it because nobody knew it existed.
What's at stake
Agents with reach into Microsoft 365 data acting for whoever asks, outside any inventory, with no check between the prompt and the action.
- 01Discover
Find every agent in the tenant, with an owner.
Connect the Microsoft 365 Copilot and Copilot Studio connector and every agent in the tenant lands in the registry: the owner, the scope, the actions it can call, and its governance coverage. Each agent shows as enforced, governed, observed or dark, so the ones with no policy stand out first.
Microsoft 365 Copilot and Copilot Studio connector · owner, scope and policy per agent · coverage: enforced / governed / observed / dark
agent discovery · overview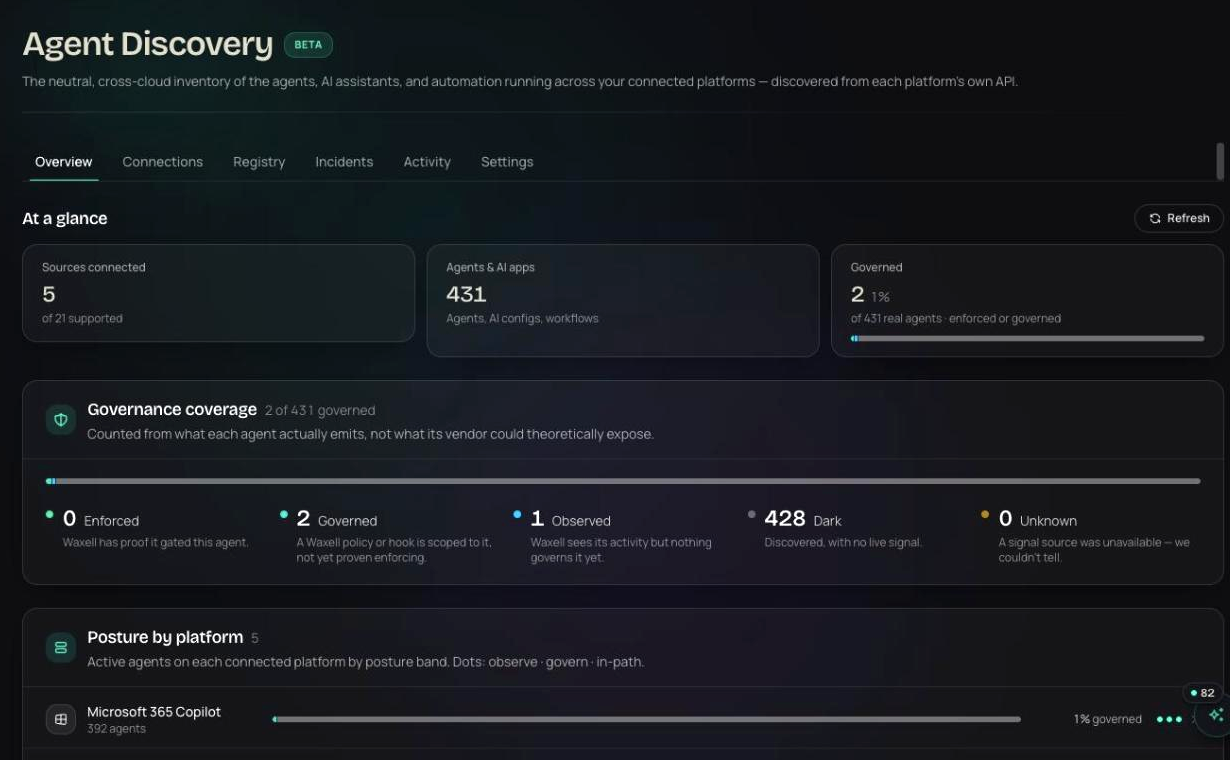
- 02Enforce
A hook in the agent. A check before every action.
Waxell installs governance hooks into each Copilot Studio agent. Before an action runs, the hook checks it against policy: who is asking, what the action reaches, what it returns. A GetMyDetails call for someone else's record is denied, and the agent gets the deny instead of the data. The rules live in the plane, so changing them does not mean editing the agent.
hook checked against policy before each action · deny proof on GetMyDetails · verdicts allow / hold / block
govern · policies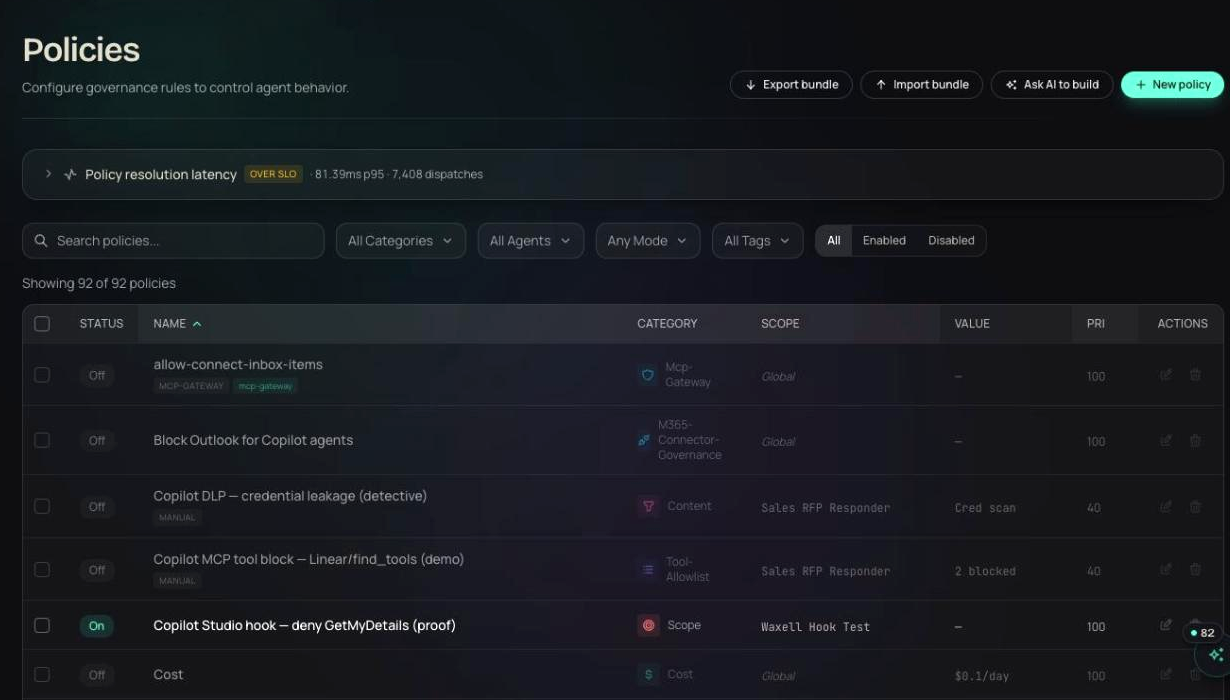
- 03Prove
Show the deny itself.
Each hook decision is a record with the agent, the action, the asker and the policy that answered. The compliance pack maps those records to the controls an auditor asks about, and the registry shows the owner of each agent in the tenant.
decision per action · owner per agent in the registry · signed compliance pack
insights · compliance pack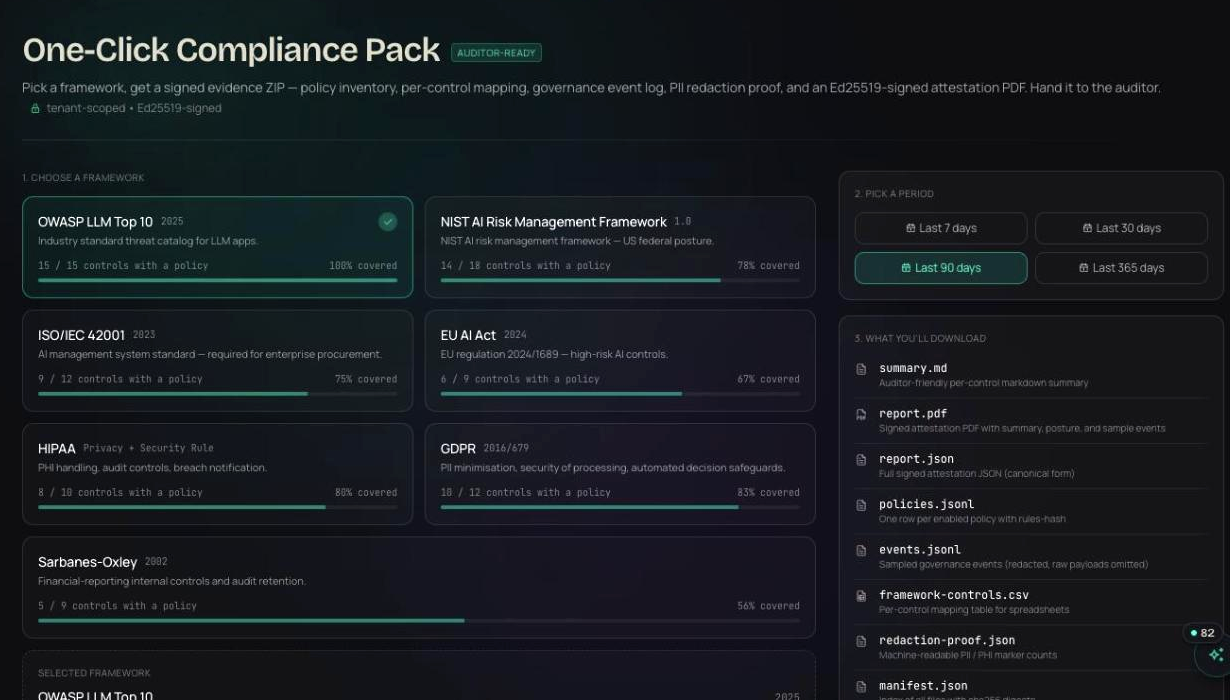


- GetMyDetails · asker j.park · subject j.parkcopilot-studio · hr-helper · scope: own recordallow
- GetMyDetails · asker j.park · subject c.riveracopilot-studio · hr-helper · scope policy · not the asker's recordblock
- CreateTicket · ServiceNowcopilot-studio · it-requests · tool allowlistallow
- SendEmail · external recipientcopilot-studio · sales-brief · data egress · routed to agent ownerhold
Illustrative entries in the shape the product writes them.
Products in this play
No. Waxell installs the governance hooks into the agents that already exist. The agent keeps its topics and actions; the hook adds a policy check before each action runs.
Run this play this week.
Free for your first agents and devices, live in about thirty seconds. Or walk through it with someone who has run it before.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF