
Play · Developers and platform teams
Agents that act for a person
The record names the personeach agent acts for.
Every agent gets an identity of its own, linked to the person it acts for, and a delegation that says what it may do on each connected app. The grant is never wider than the person's, the record shows both names, and revoking it takes one action.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF

- This play uses
- 01Discover
- 03Enforce
- 05Prove
Who
A platform team shipping an assistant that reads a user's calendar, files tickets, and sends messages on their behalf through a shared service account.
What happened
Security asked which human was behind a Slack message the assistant sent, and the answer was 'the bot user, for everyone'.
What's at stake
A service account with everyone's reach, actions that cannot be attributed to a person, and offboarding that leaves an agent's access behind.
- 01Discover
Name every agent and who it acts for.
Register each agent with an identity of its own. The identity overview shows every agent, the person it acts for, and the apps it is connected to. Where an agent serves end users, sub-user tokens attribute each action to the specific user, so 'the bot did it' stops being an answer.
identity per agent · person per agent · sub-user tokens · app connections listed
identity · overview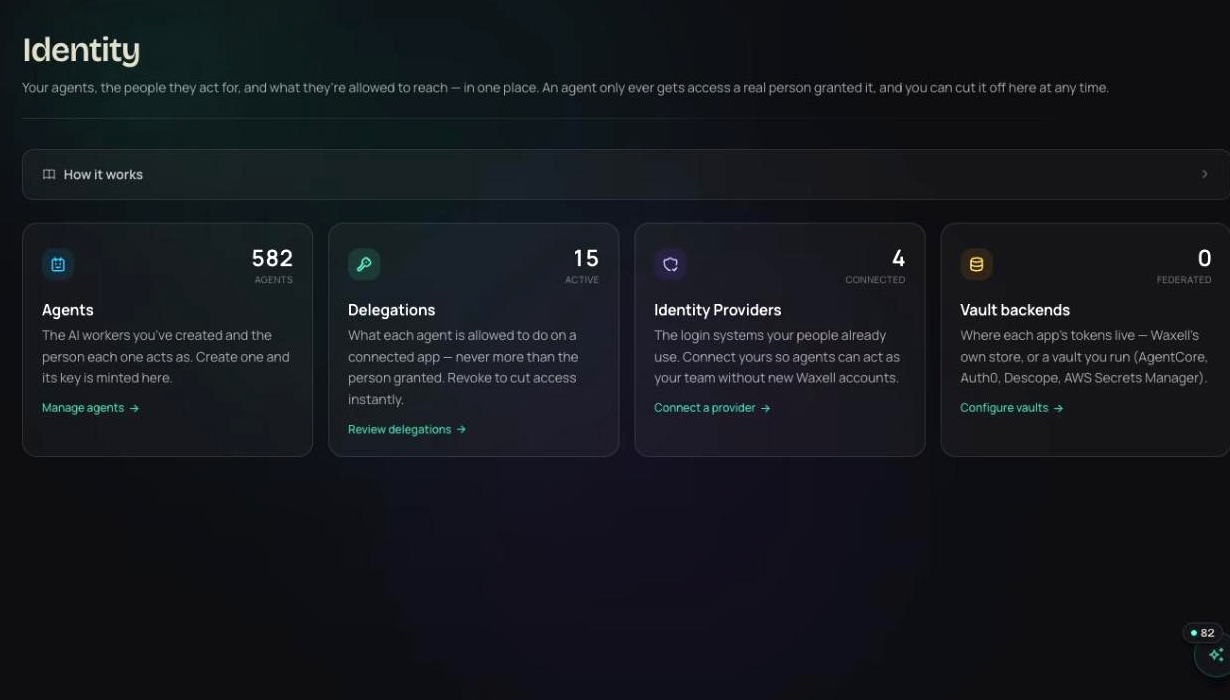
- 02Enforce
A delegation is a ceiling, not a key.
A delegation says what an agent may do on a connected app: read the calendar, create tickets, post to two channels. It can never be wider than what the person granted. The app token sits in a vault, Waxell's store or your own AgentCore, Auth0, Descope or AWS Secrets Manager, so the agent holds a scoped token and never the secret. Each action is checked against the delegation before it goes out; outside it, the call is blocked or held for the person. Revoke a delegation and the next call fails; offboard the person through SCIM and every grant goes with them.
delegation per app · never wider than the person · vault backends · revoke instantly · SCIM offboarding
govern · policies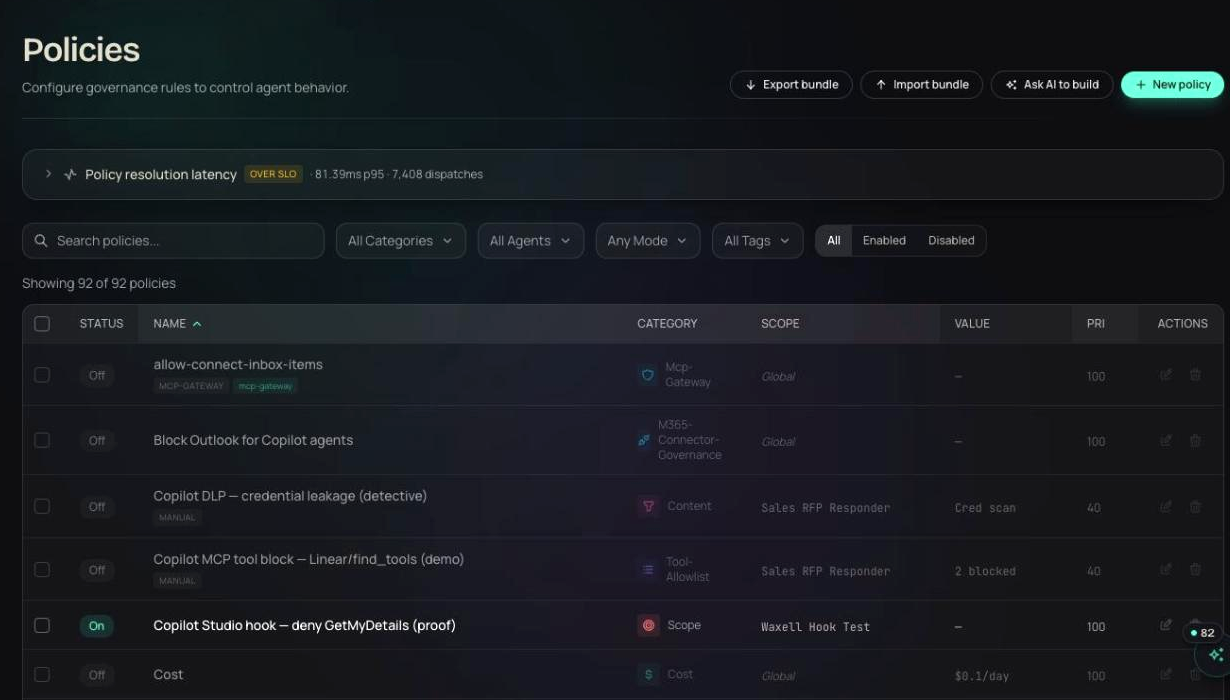
- 03Prove
Two names on every row.
Each record carries the agent, the person it acted for, the delegation that allowed it, and the verdict. When security asks who sent the message, the answer is a row with both identities. The compliance pack maps the same evidence to the accountability and oversight controls in the EU AI Act and ISO/IEC 42001.
agent and person per record · delegation named · signed compliance packs
insights · compliance pack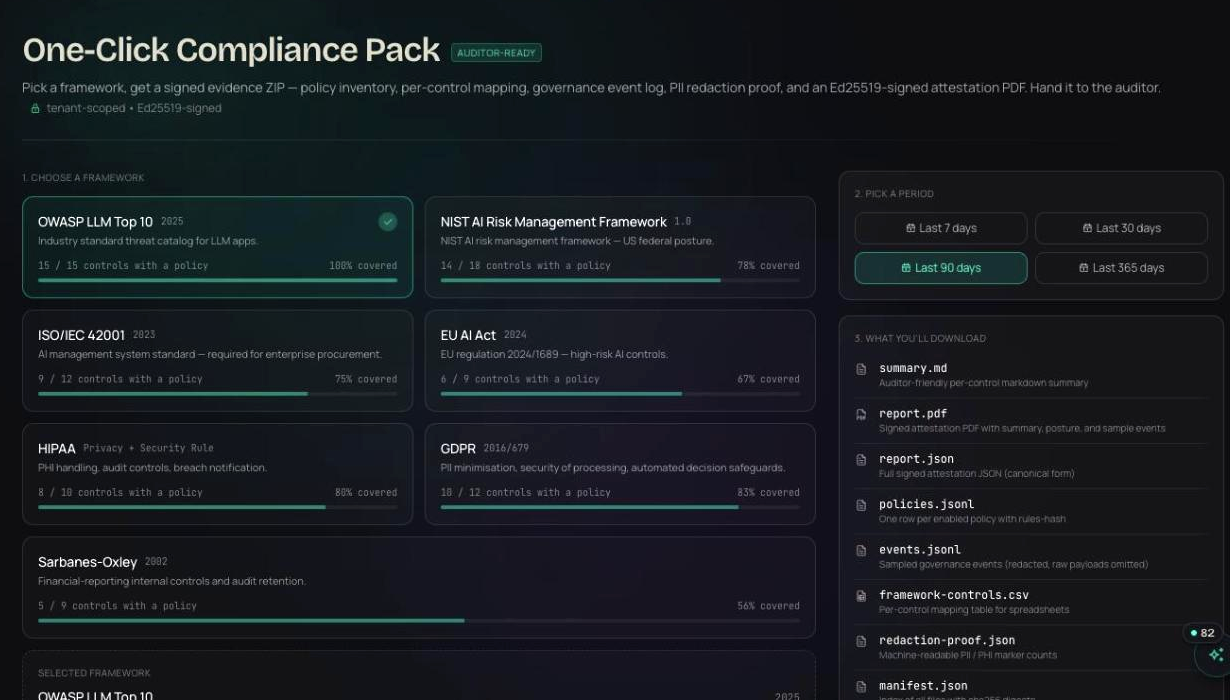


- google.calendar.list · next 7 daysassistant · for t.alvarez · delegation: calendar readallow
- slack.post · #eng-oncallassistant · for t.alvarez · delegation: post to 2 channelsallow
- slack.post · #execassistant · for t.alvarez · outside delegation · t.alvarez has no accessblock
- jira.create_issueassistant · for r.chen · r.chen offboarded · grants revoked with SCIMblock
Illustrative entries in the shape the product writes them.
Products in this play
No. A delegation is bounded by what the person granted, and a call outside it is blocked or held for them. If the person loses access to an app, the agent loses it in the same moment.
Run this play this week.
Free for your first agents and devices, live in about thirty seconds. Or walk through it with someone who has run it before.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF