
Play · MSPs and resellers
Roll governance to every client
Build the policy once,dry-run it on each client,then apply it.
Reseller access flips between client tenants from one console. Guard export and import carries a policy set from the client where you got it right to every other one, with a dry-run plan before anything changes.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF

- This play uses
- 01Discover
- 03Enforce
- 05Prove
Who
An MSP running security for forty clients, each with its own tenant, each asking for AI governance this quarter.
What happened
The first client's endpoint rollout took a week of tuning. Thirty-nine more at that pace is not a service, it is a backlog.
What's at stake
Policy that drifts between clients, a technician editing forty consoles by hand, and nothing to hand over when a client's auditor asks for evidence.
- 01Discover
Deploy per client from one console.
Reseller access flips between client tenants without separate logins. Push the endpoint agent through each client's MDM or RMM (Jamf, Kandji, Intune, Hexnode, NinjaOne and others) and the browser extension by policy, and each tenant fills with its own inventory: AI apps, extensions, CLIs, personal versus corporate accounts, mapped to owners. If a client runs agents on Hatz AI or in Microsoft 365, the discovery connectors put those in the same registry.
reseller access across tenants · Jamf, Kandji, Intune, Hexnode, RMMs · Hatz AI and Microsoft 365 connectors
endpoints · needs attention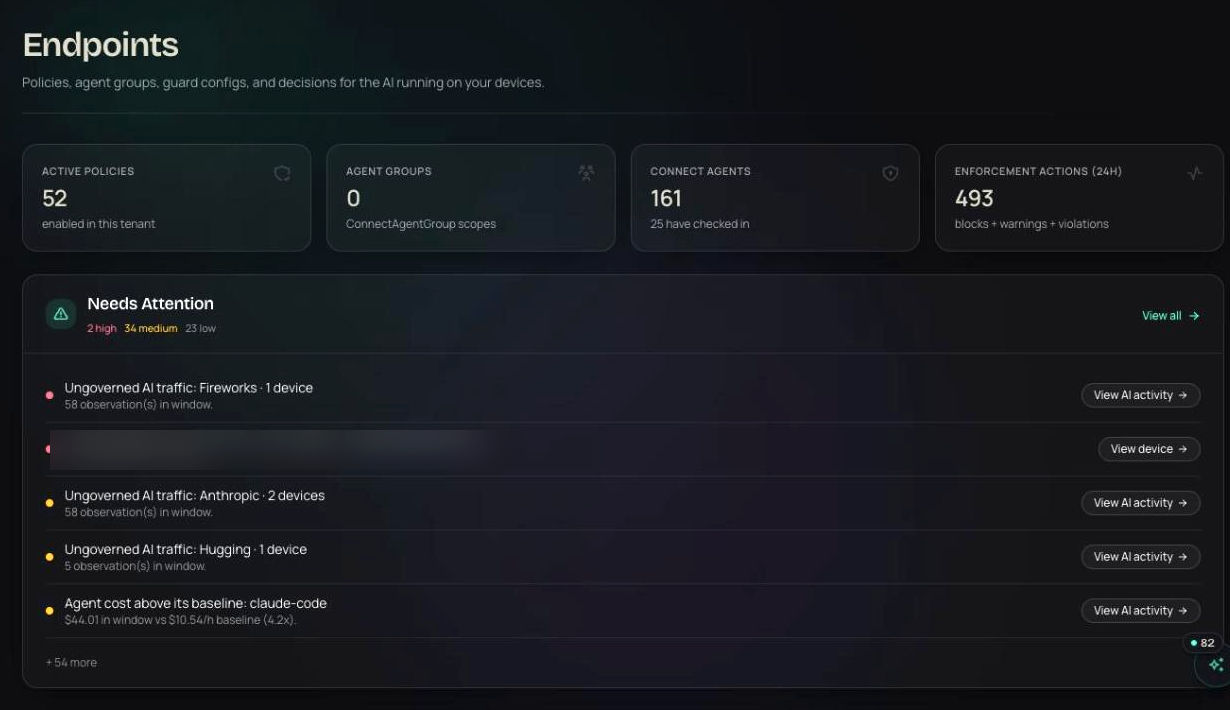
- 02Enforce
Export the guards that work. Dry-run them on the next client.
Tune the Guard and DLP rules on one client until they are right. Export the guard set, import it into the next tenant, and read the dry-run plan: which rules would be created, changed or left alone. Apply when the plan reads the way you expect. Rules stay per client after that, so a law firm's block list and a marketing agency's do not have to match.
guard export and import · dry-run plan before apply · rules per tenant
govern · policies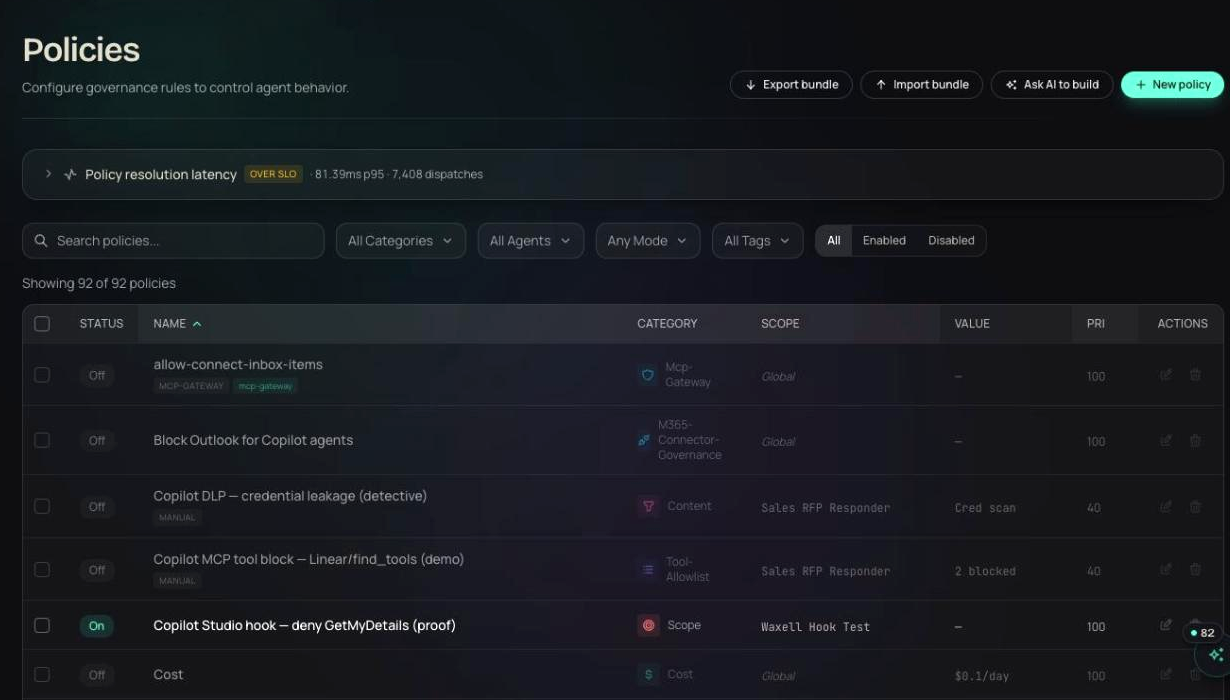
- 03Prove
Each client gets its own report.
Every tenant keeps its own decision record, its own Shadow AI report and its own signed compliance pack, so a client's auditor sees only that client. If you run HaloPSA, the integration puts the work where your technicians already are.
per-client evidence · per-client Shadow AI report · signed compliance pack · HaloPSA integration
insights · executive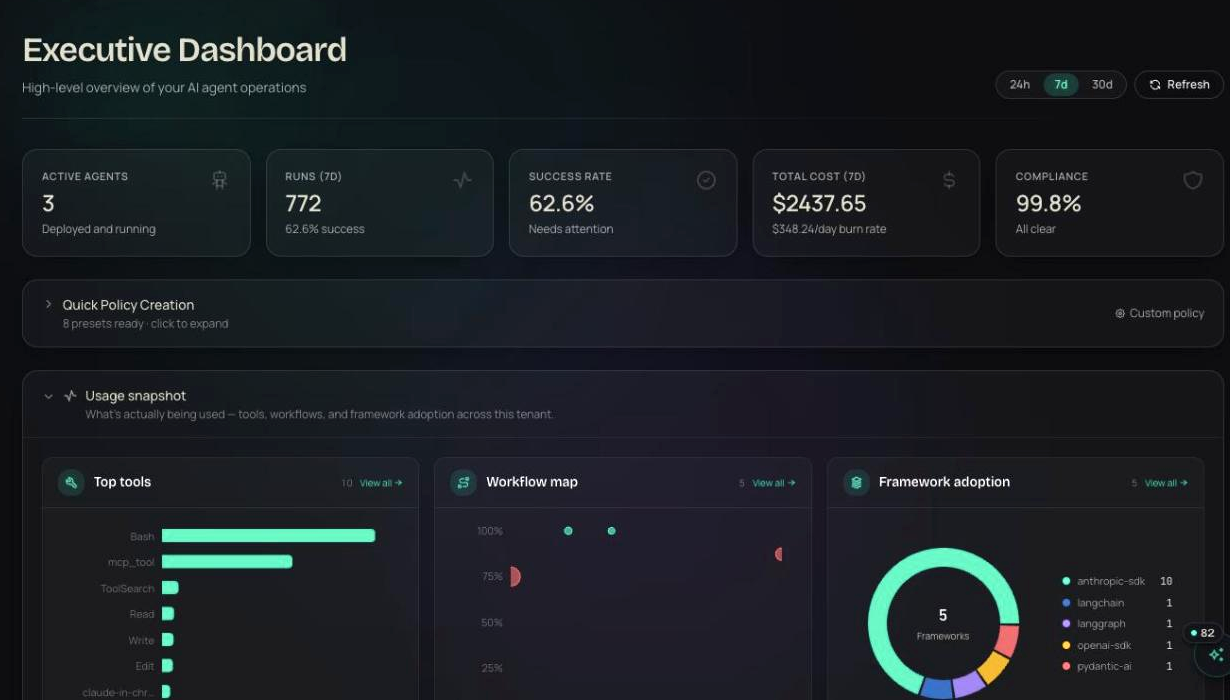


- guard import · dry-run plantenant · northfield-law · 12 create · 3 update · 0 removeallow
- guard import · applytenant · northfield-law · 15 rules applied by t.moralesallow
- ChatGPT · personal account · paste 2,400 charsendpoints · northfield-law · a.reyes-win · client matter PII · personal accountblock
- guard import · dry-run plantenant · brightline-media · 9 create · 6 update · 0 removeallow
Illustrative entries in the shape the product writes them.
Products in this play
No. Reseller access flips between client tenants from one console. Each client stays its own tenant with its own data; you move between them.
Run this play this week.
Free for your first agents and devices, live in about thirty seconds. Or walk through it with someone who has run it before.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF