
Play · Developers and platform teams
Govern an inherited agent
An agent nobody on the team wroteis under policy by the end of the day.
Name the agent in waxell.init() and Observe traces its model calls, tool calls, tokens and cost, then checks your policies at the start of each run and before each model call, tool call and MCP call. The agent's logic does not change, and you learn what it does before you decide what it may do.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF

Who
A platform team that inherited a Python invoice-triage agent when its author changed teams: a LangChain chain, three tools, an OpenAI key in an environment variable.
What happened
Finance asked what the agent can do to a vendor record, and the only documentation was the code.
What's at stake
An agent in production that nobody can describe, with tool access nobody reviewed and spend nobody capped.
- 01Observe
Two lines. Name it, or it is not governed.
pip install waxell-observe, then import waxell_observe as waxell and call waxell.init(agent_name="invoice-triage") at startup. The AI libraries installed in the environment are instrumented on init, from model providers to agent frameworks to vector databases, out of 160+ instrumentors, along with HTTP clients, databases and caches. The name matters: without agent_name, or the WAXELL_AGENT_NAME environment variable, the agent is traced but no policy can apply, and the SDK logs a warning that says so.
waxell.init(agent_name=...) · 160+ instrumentors · infrastructure libraries on by default · no change to the agent's logic
observe · executions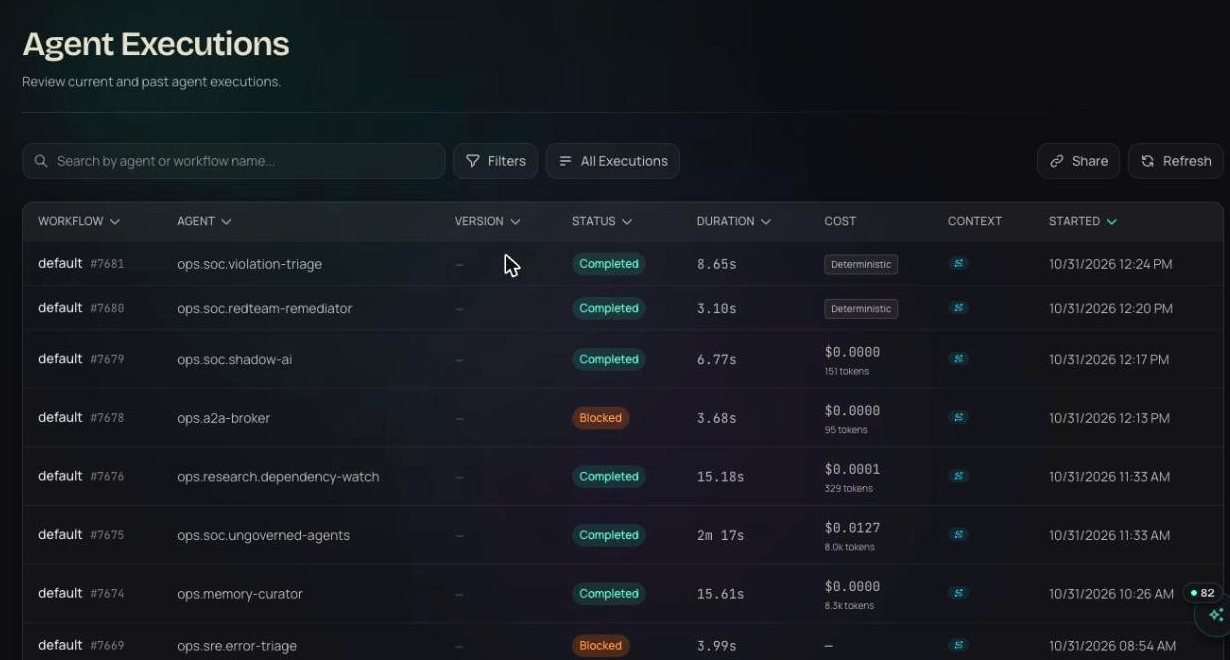
- 02Observe
Read what it actually does.
Each run lands with its model calls, its tool calls and their arguments, tokens, latency and cost in dollars. The tools it calls, the models it uses and what a run costs come from the runs themselves, not from reading the code. Prompt and response content is captured by default; pass capture_content=False if this agent handles data you don't want stored.
tool calls with arguments · model, tokens, latency and cost per call · capture_content on by default
observe · run trace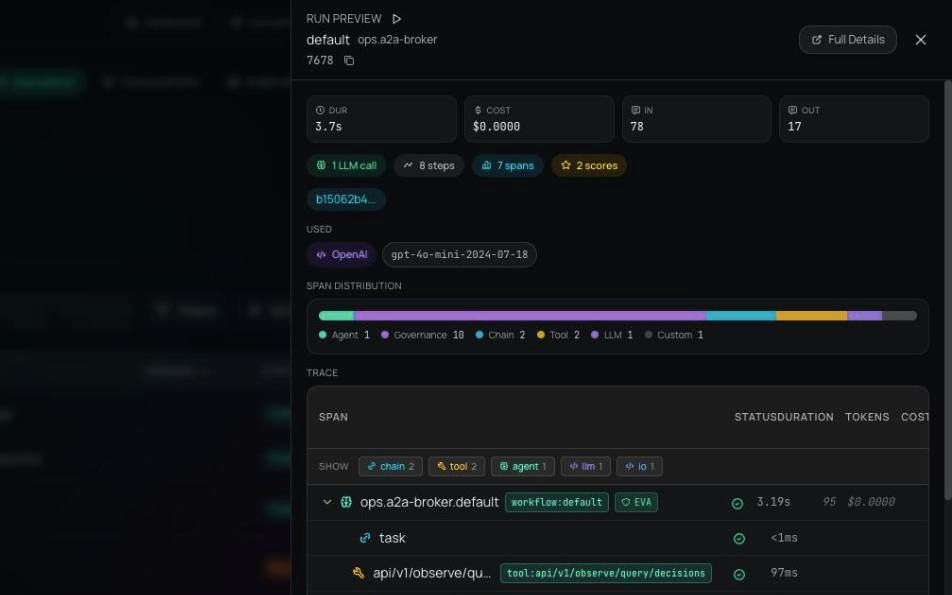
- 03Enforce
Policy before the call, not after it.
With the agent named, the SDK fetches its policies and checks them at run start and before each model call, tool call, MCP call and sub-agent spawn. A tool allowlist stops a call to update_vendor_bank_details before it executes. A budget is checked before each model call. The kill switch is checked when a run starts, so once it is flipped the agent does not start again. Waxell also suggests limits from the agent's last seven days of runs: token and cost budgets, a timeout and a step limit, each at twice the observed average.
checked at run.start, llm.before, tool.before, mcp.before and spawn.before · kill switch at run start · suggested limits at 2x the 7-day average
govern · policies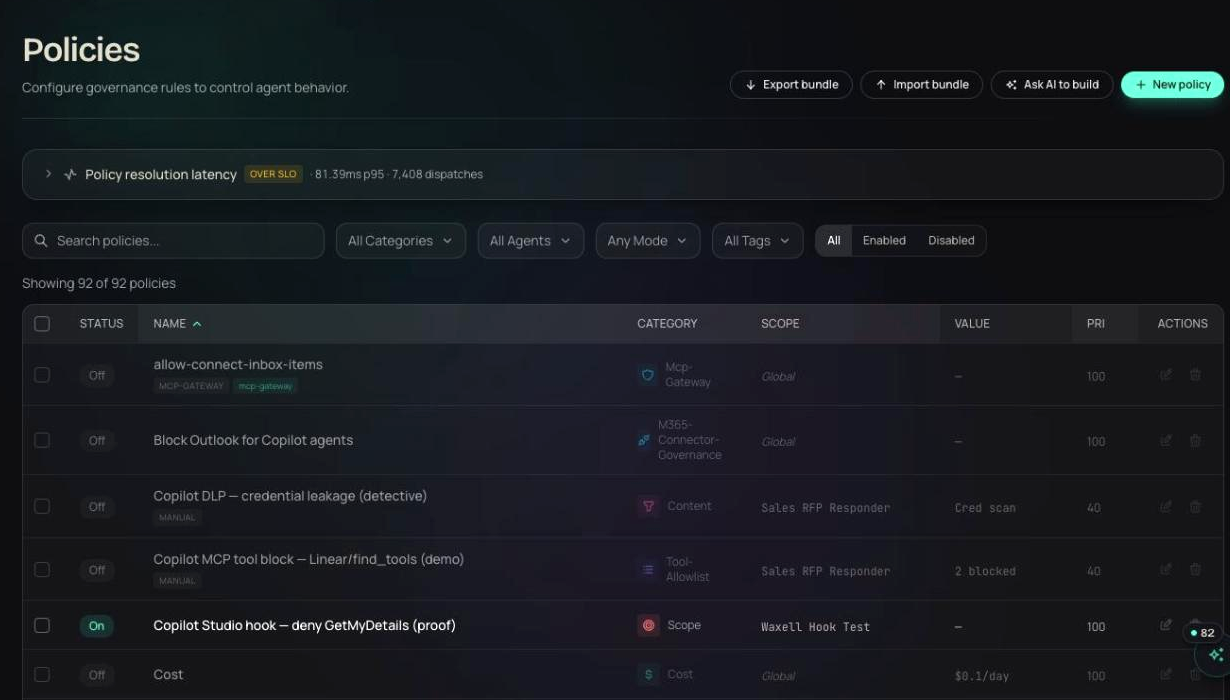
- 04Enforce
Decide what happens if Waxell can't be reached.
By default the SDK fails open: if policies can't be fetched, the agent keeps working, ungoverned, rather than breaking because governance had a problem. Set WAXELL_SURFACE_GATE=closed and the preventive checks block instead, so taking the control plane offline cannot become a way around policy.
fail open by default · WAXELL_SURFACE_GATE=closed or WAXELL_GATE_FAIL_CLOSED=1 · preventive checks block when closed


- openai.chat · 3,410 in · 290 out · $0.021invoice-triage · run 2210 · traced · within budgetallow
- tool update_vendor_bank_detailsinvoice-triage · run 2214 · tool allowlist · not an approved toolblock
- run start after the kill switch flippedinvoice-triage · run 2231 · kill switch · checked at run startblock
- Cost Budget · $0.18 per runrecommendations · invoice-triage · 2x the 7-day average · waiting for reviewhold
Illustrative entries in the shape the product writes them.
Products in this play
Two lines at startup: the import and waxell.init(agent_name=...). The agent's logic, prompts and tools stay as they are. If it runs on a framework Observe instruments, the framework's runs and tool calls are picked up on their own.
Run this play this week.
Free for your first agents and devices, live in about thirty seconds. Or walk through it with someone who has run it before.
30 minutes. No commitment.
SOC 2 Type II attested · ISO/IEC 27001:2022 certified · HIPAA with a BAA · aligned to the EU AI Act and NIST AI RMF